OpenAI said the May 11, 2026, supply chain attack involving TanStack’s npm packages affected two employee devices and led to limited credential theft from internal source code repositories. The company said it was rotating application-signing certificates as a precaution.
OpenAI said its investigation found no evidence that customer data had been accessed, production systems or intellectual property had been compromised, or its published software had been altered. It also said it had not identified misuse of the affected credentials or follow-on access by the attacker.
The company reported unauthorized access and credential-focused exfiltration activity in a limited subset of repositories accessible to the two employees. OpenAI said only limited credential material was successfully taken and no other information or code was affected.
Certificate rotation and the macOS update deadline
OpenAI said it isolated affected systems and accounts, revoked user sessions, rotated credentials across the affected repositories and temporarily restricted deployment workflows. It also engaged a third-party digital forensics and incident response firm.
The affected repositories contained signing certificates for OpenAI products. The company identified signing material for macOS, Windows, iOS and Android as impacted, but said it had found no evidence that its certificates had been used to sign malicious software. It said it was coordinating with platform providers to prevent unauthorized use.
OpenAI’s notice set June 12, 2026, as the deadline for macOS users to update their applications. The company said revoking the previous certificate could cause macOS security protections to block new downloads and first-time launches of applications signed with it. Windows and iOS users did not need to take action, OpenAI said.
How TanStack’s packages were compromised
In its postmortem, TanStack said an attacker published 84 malicious versions across 42 packages in its Router/Start repository between 19:20 and 19:26 UTC on May 11. TanStack said all affected versions were deprecated within an hour and removed by npm shortly afterward. It said its other repositories and packages were unaffected.
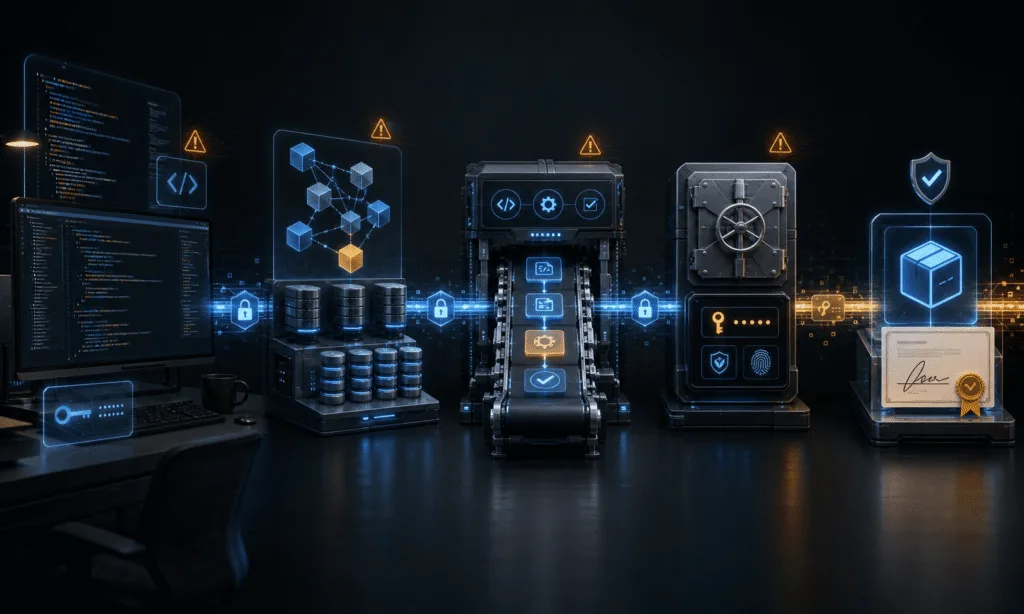
TanStack described an attack that combined a GitHub Actions workflow running code from an external pull request, poisoning of a shared build cache and extraction of an OpenID Connect authentication token from a release runner’s memory. The attacker then used that token to publish malicious packages directly to npm, bypassing the workflow’s normal publishing step, TanStack said.
TanStack said the initial compromise did not involve theft of a maintainer’s npm publishing token. Its analysis described malicious package versions that could execute a payload during installation through an added optional dependency and its prepare script.
Researchers at StepSecurity and Socket described malware targeting developer and cloud credentials, including GitHub tokens, npm publishing tokens, AWS credentials, Kubernetes secrets and SSH keys. They also identified persistence mechanisms involving Claude Code hooks and VS Code tasks. Those campaign findings do not establish that the same persistence mechanisms ran on OpenAI’s affected devices.
A wider campaign across npm and PyPI
The broader Mini Shai-Hulud campaign involved packages associated with TanStack and Mistral AI, as well as Guardrails AI and other projects. The affected packages and payloads did not all behave identically.
Mistral AI said compromised versions of its three npm SDK packages contained a broken dropper: the loader referenced a filename that did not match the included payload, preventing that payload from executing. The company said the compromised versions were removed from npm.
A separate Mistral AI advisory identified malicious code in the mistralai 2.4.6 Python package. It said the dropper ran on Linux when applications imported modules under mistralai.client, rather than simply installing the package. The advisory did not assess the downloaded second-stage payload.
Guardrails AI separately said an attacker published malicious version 0.10.1 of its Python package using deployment tokens obtained after an employee’s GitHub personal access token was compromised. The company said its log review found no evidence of user data exfiltration through its systems.
Microsoft Threat Intelligence described the Linux payload associated with mistralai 2.4.6 as a credential stealer. It said the payload avoided Russian-language environments and contained a destructive branch with a one-in-six chance of executing a recursive deletion command when a system appeared to be in Israel or Iran. That assessment described malware capabilities; it did not establish successful credential theft from affected Python-package users or that the component ran on OpenAI’s devices.