A toolkit called ConsentFix v3 automates parts of an OAuth phishing attack against Microsoft accounts, including the exchange of captured authorization codes for tokens, Push Security said.
The company said a member of the XSS criminal forum released the toolkit, building on earlier ConsentFix implementations. It described v3 as closer to a proof of concept than a large-scale phishing service. Whether this version had gained traction in criminal campaigns remained unclear.
Automating token exchange after authentication
Push Security first described ConsentFix in December 2025 after detecting a campaign targeting Microsoft accounts through the Azure CLI application. The technique combines ClickFix-style social engineering with abuse of the OAuth 2.0 authorization code flow. Researcher John Hammond subsequently demonstrated a version that replaced copying and pasting with a drag-and-drop interaction.
In the described attack, a phishing page opens a legitimate Microsoft authorization page. After the user authenticates or selects an existing signed-in account, the browser redirects to a localhost address containing an authorization code. The phishing page then prompts the victim to paste or drag that address into the attacker-controlled page.
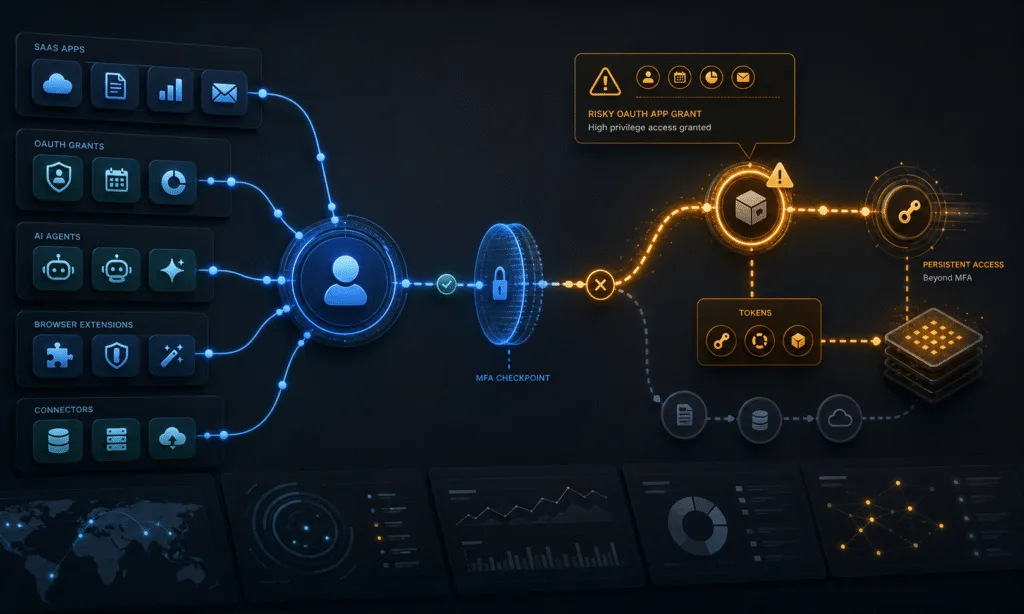
The attacker can exchange the captured code for tokens permitting access to Microsoft resources. Push Security said users already signed in to Microsoft may only need to select their account, without entering credentials or completing another multifactor authentication challenge. The technique therefore captures authorization material after legitimate authentication.
Push Security said v3’s workflow covers preparing infrastructure, researching targets, creating personas and managing phishing emails. Its analysis identifies Cloudflare Workers for hosting, ZoomInfo for target identification and Dropbox for hosting PDFs.
The company described Pipedream as the automation component: a webhook receives captured authorization material, and a workflow exchanges it for a refresh token. This automates token handling after the victim shares the URL; the social engineering step remains necessary.
Access depends on applications and permissions
ConsentFix targets Microsoft first-party applications with pre-consented permissions. Push Security said the resulting access depends on the targeted application, its scopes and the victim’s permissions. Applicable tenant policies also affect which resources an attacker can reach.
Microsoft’s Family of Client IDs mechanism can extend the usefulness of captured tokens. A family refresh token obtained for one application can be redeemed for access tokens associated with other applications in the same family. Access remains subject to the permissions available to the application and user.
Push Security identified SpecterPortal as a tool used for activity after compromise. Depending on the tokens and permissions obtained, that activity may include accessing email, files and other Microsoft-connected resources.
Push Security reportedly said its v3 testing relied on personal Microsoft accounts. That reported limitation restricts what the tests establish about enterprise environments, where permissions, available services and tenant settings affect the potential impact.
Application restrictions and detection limits
Push Security recommended creating service principals for affected first-party applications and restricting access to authorized users. It cautioned that an assigned user who is phished can still expose access through the technique.
The company also recommended examining application and resource identifiers in logs and comparing the initial sign-in with subsequent activity. Initial authentication occurs in the victim’s browser and can show the user’s legitimate network address, while later token use may originate from attacker infrastructure.
Microsoft describes token protection as a control that reduces token replay by requiring device-bound sign-in session tokens. Its applicability depends on supported clients, resources and configurations, so coverage cannot be assumed across every application targeted by ConsentFix.