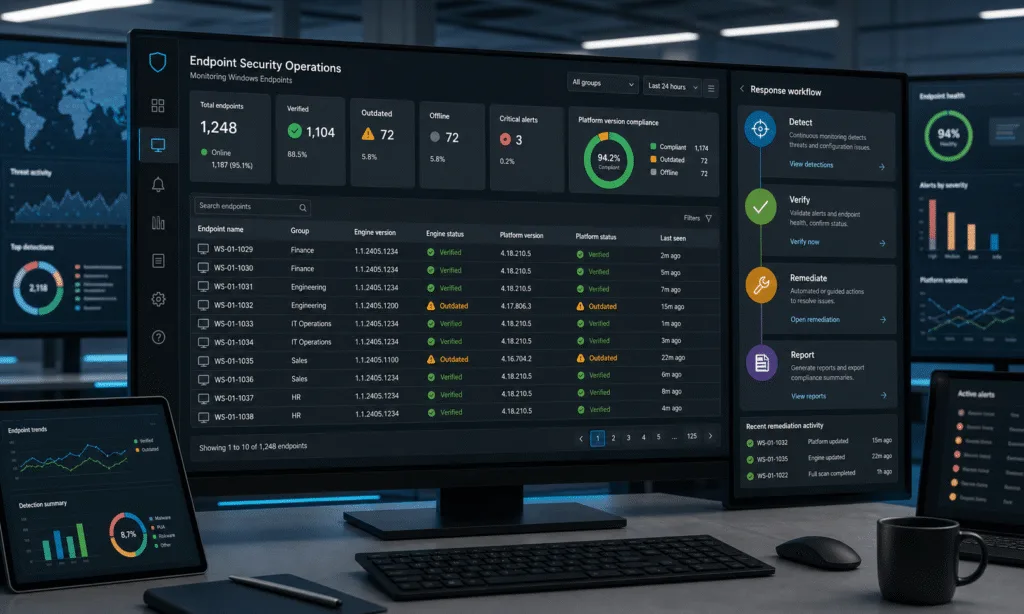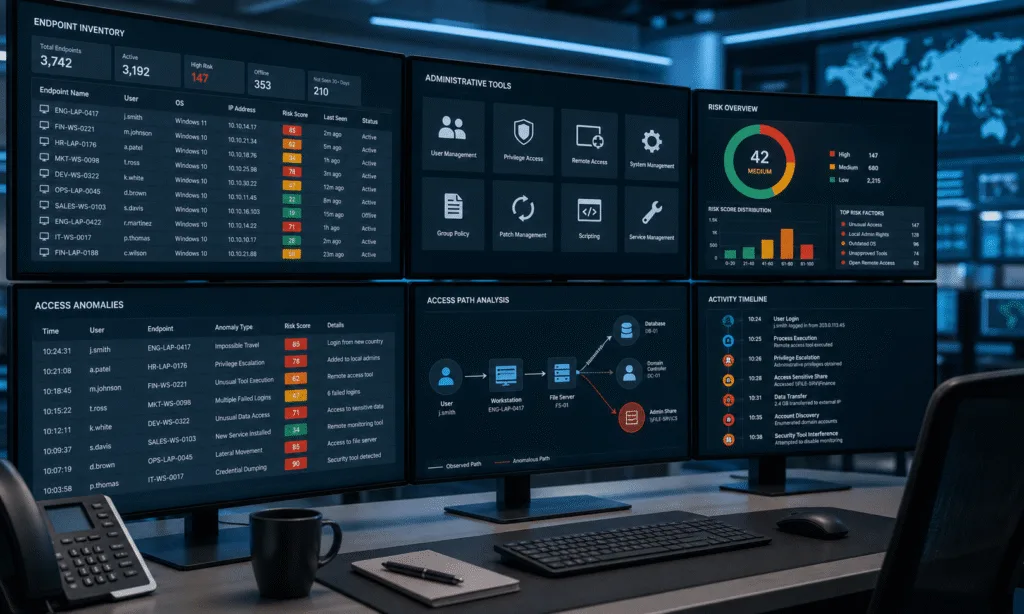
Bitdefender is offering a free, 45-day Internal Attack Surface Assessment that it says identifies unnecessary access to legitimate applications and system utilities that attackers can misuse. The company announced the program on March 31, 2026.
The company’s materials differ on eligibility. Its launch announcement specifies organizations with 250 or more employees, while an undated enrollment page specifies 250 or more users in the United States, Europe or Asia-Pacific. Employees and users are different measures of organization size.
The assessment focuses on tools that support ordinary administration and software development, including PowerShell, WMIC, Certutil, netsh and MSBuild. Attackers can also abuse legitimate utilities to execute commands, move between systems or interfere with security controls. Using existing system tools during an attack is commonly described as living off the land.
Behavioral learning and optional restrictions
The program uses GravityZone PHASR, short for Proactive Hardening and Attack Surface Reduction. Bitdefender says PHASR builds behavioral profiles for individual user-machine combinations, comparing observed activity with threat intelligence to identify access that may be unnecessary.
The assessment page describes a learning period of about 30 days. Broader PHASR documentation gives a range of 20 to 60 days depending on the monitored application, with accelerated learning for GravityZone EDR and XDR customers. The approximately 30-day period is therefore the assessment’s stated workflow rather than a fixed duration for every deployment.
Bitdefender lists five assessment categories: living-off-the-land binaries, remote administration tools, tampering tools, cryptocurrency miners and software piracy tools. The company says reporting maps exposure to users and devices and prioritizes recommendations for restrictions.
Organizations can apply restrictions manually or use PHASR’s Autopilot mode for automated enforcement. Bitdefender says the controls can restrict an entire application or particular actions within it, allowing some functionality to remain available.
Access restoration is configurable. Bitdefender’s December 2025 product documentation describes an option allowing users to request access to blocked applications or actions and provide a business justification. Administrators can review the request and approve or deny access.
Coverage beyond Windows
Although many of the utilities discussed are associated with Windows, Bitdefender described PHASR support for Linux and macOS in an April 25, 2026 product update.
The company says coverage across Windows, macOS and Linux is available through Bitdefender Endpoint Security Tools within the full GravityZone stack. It separately describes a standalone PHASR agent for Windows and macOS for use alongside third-party security products. Those deployment options do not establish identical platform coverage for every configuration.
Research and performance claims
Bitdefender’s rationale draws on internal research published on June 3, 2025. Bitdefender Labs said it analyzed 700,000 security incidents from GravityZone alongside 90 days of legitimate-use telemetry. It reported that 84% of high-severity incidents involved living-off-the-land binaries. That finding concerns the high-severity subset of its research, rather than all 700,000 incidents or cyberattacks generally.
The researchers also reported PowerShell activity on 73% of endpoints in their dataset. They said third-party applications frequently invoked PowerShell without displaying an interface, showing that observed tool use could reflect application activity as well as direct administrative work.
Bitdefender markets the assessment as requiring minimal effort and avoiding operational disruption. Its launch announcement also claims organizations can reduce their attack surface by up to 95%. These are company assertions about the program’s operation and potential results, rather than guarantees for individual deployments.