ThreatFabric says a variant of the TrickMo Android banking malware routes its primary command-and-control traffic through The Open Network (TON) and adds tools for probing networks and forwarding traffic through infected phones.
The company identified and began tracking the variant, labeled TrickMo.C, between January and February 2026 in campaigns targeting banking and cryptocurrency wallet users in France, Italy and Austria. Its geographic assessment rests on campaign tags in the malware’s telemetry and does not establish the full extent of targeting.
ThreatFabric describes TrickMo.C as a redesign of an existing malware platform, with changes to its communications and network functions alongside familiar credential-theft and remote-control capabilities. The company also described campaigns using apps disguised as TikTok or streaming services.
Command traffic through TON
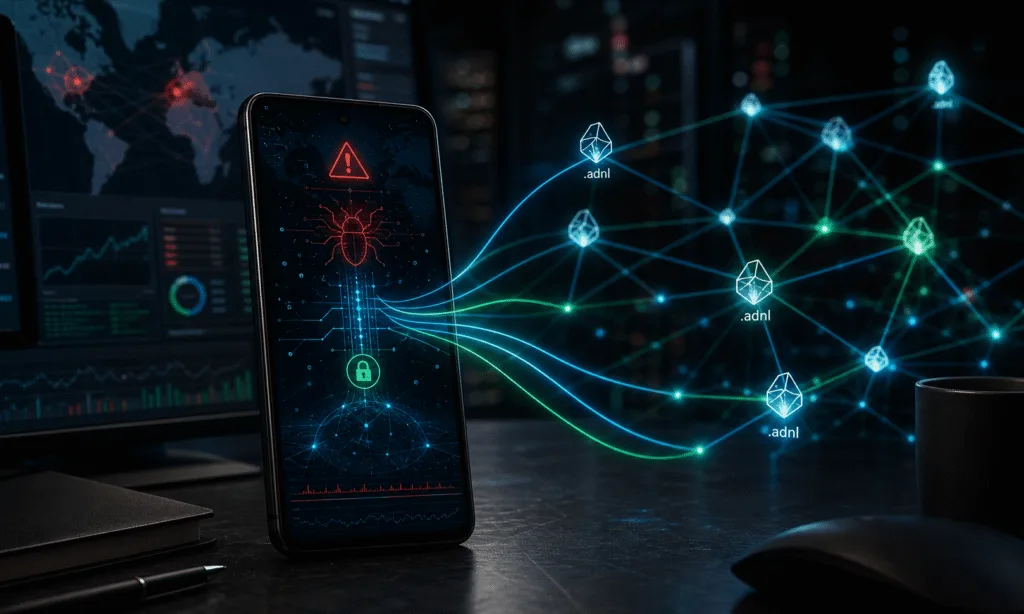
ThreatFabric said the host Android application package, or APK, starts an embedded TON proxy on a local loopback port. The malware routes command-and-control requests through that proxy to .adnl addresses within the TON network. For the limited public-internet hostnames it still needs, the malware uses DNS-over-HTTPS instead of the device’s local DNS resolver.
The researchers said this arrangement makes conventional domain takedowns largely ineffective because the command endpoints do not depend on the public DNS hierarchy. They also said the encrypted traffic resembles legitimate TON activity at the network edge, complicating detection based on traffic patterns.
TON is a legitimate decentralized networking and blockchain platform. TON Sites use abstract ADNL addresses, and traffic between the proxy and a site is encrypted at the ADNL layer. Server IP addresses remain published in TON’s distributed hash table for routing, even though they are not exposed at the HTTP layer. ThreatFabric characterized the malware’s use of TON as abuse by third-party operators.
Network reconnaissance and traffic forwarding
ThreatFabric describes a two-stage architecture in which the host APK provides loading and persistence, while a separate APK module named dex.module is downloaded and loaded at runtime to deliver core attack functions. Earlier TrickMo versions also used this modular design.
The researchers identified new network commands including curl, dnsLookup, ping, telnet and traceroute. These provide HTTP probing, DNS lookups, reachability checks, TCP connection testing and route tracing from the infected handset’s network position. The dnsLookup function uses the device’s platform resolver, allowing operators to examine name resolution on the network to which the phone is connected.
The variant also supports SSH local and remote port forwarding and an on-device SOCKS5 proxy protected by a username and password, ThreatFabric said. The researchers described combining the proxy with a remote-forward tunnel to make the handset a traffic exit point, with outbound connections originating from the victim’s IP address.
ThreatFabric said these functions could give operators access to resources reachable from the phone’s home or corporate network and undermine fraud checks that depend on IP addresses. The findings describe those capabilities without establishing how widely operators have used them in attacks.
Retained capabilities and inactive components
ThreatFabric said TrickMo retains credential phishing through full-screen overlays that imitate banking apps, keylogging, screen recording and live streaming, and remote interaction through Android accessibility services. The malware pressures users to grant accessibility-service permission, which enables operators to interact with the device.
The reported functions also include SMS and notification interception, suppression of one-time-password notifications, clipboard modification, screenshot capture and notification filtering.
ThreatFabric found that the Pine runtime hooking framework was bundled and initialized, but identified no hook installations in the analyzed code of either stage. Earlier versions had used hooking to intercept networking and Firebase-related operations.
The application also declared broad NFC permissions and reported NFC and host-card-emulation capabilities in telemetry. The researchers did not find reachable NFC functionality in either analyzed stage. Those observations do not establish that the variant was carrying out NFC-based attacks.